Watch the video
Join Patreon : https://patreon.com/ncot_tech One time donation: https://ko-fi.com/ncot_tech Website : https://ncot.uk
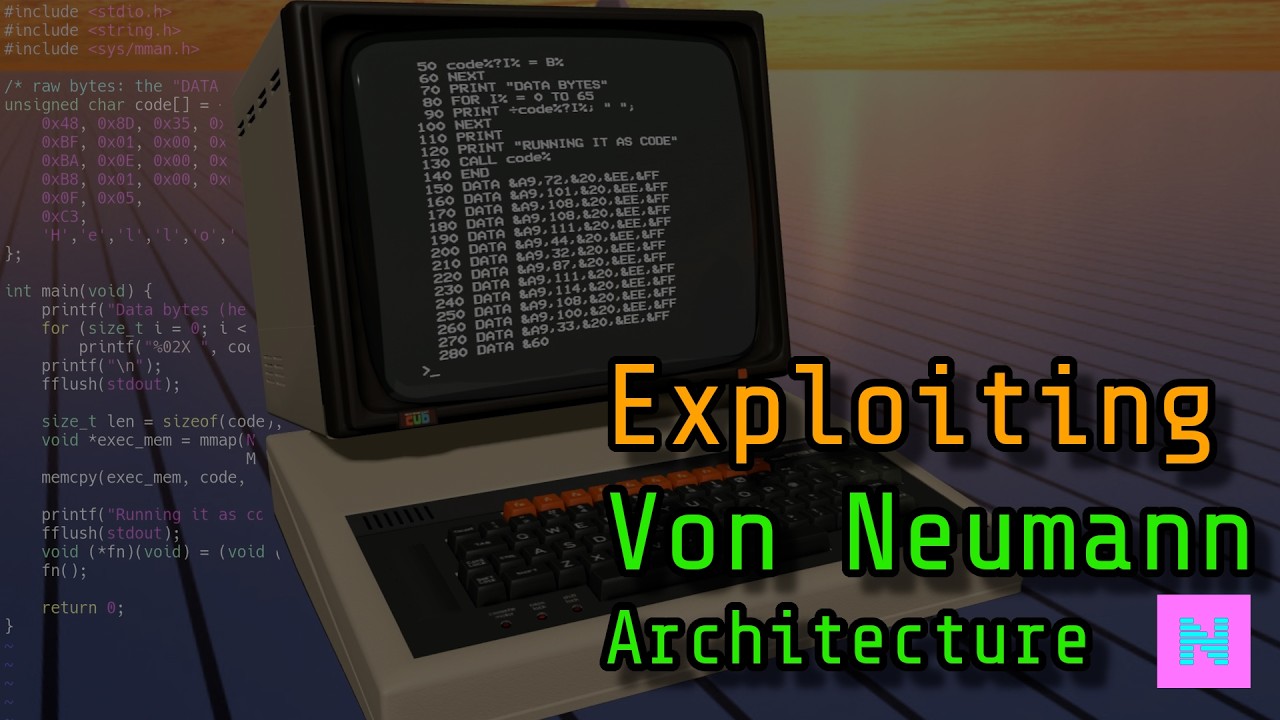
From typing in BASIC listings on a BBC Micro in the 1980s to modern x86 machine code on a PC, this video breaks down the Von Neumann architecture and the fetch-decode-execute cycle at the heart of every computer. We look at raw opcodes and ASCII data sitting side by side in memory, show how a CPU can be tricked into executing data as code, and connect that same principle to real-world exploits including the famous Super Mario World RAM manipulation TAS by Seth Bling. Along the way we cover why modern CPUs use an execute-permission bit (the NX bit) to guard against buffer overflows and code injection, how the Harvard architecture differs by physically separating code and data memory, and why this isn’t a bug but a fundamental, necessary part of how programs get loaded and run. Topics covered: Von Neumann architecture, CPU fetch-decode-execute cycle, BBC BASIC and machine code, x86 assembly, memory mapping in C, buffer overflow and code injection exploits, and hardware execute protection.
Keywords
#vonneumannarchitecture #cybersecurity #computerscience #machinecode #bufferoverflow #cpuarchitecture #retrocomputing #hacking #programming #infosec